Pentagon Probes Suspected Freezer Hacks as Europe’s Refrigeration Crisis Spreads
Pentagon officials are now looking into whether refrigeration issues that struck affected at least six commissaries is tied to cyberattacks, while several European supermarket chains are reporting temperature spikes in food storage units.
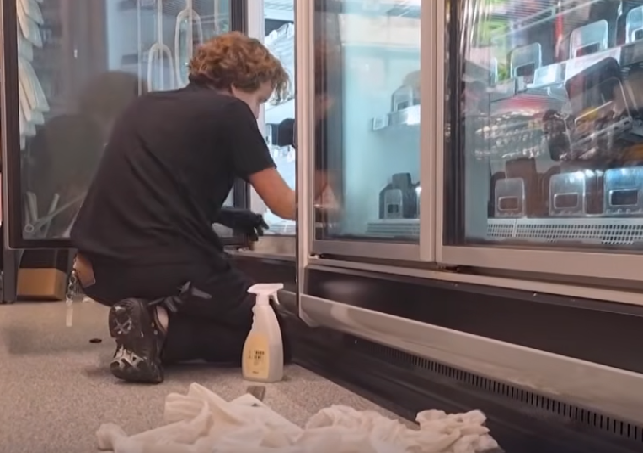
It turns out that the next “Cold War” may come with melted ice cream rather than missile silos, as the Pentagon investigates suspected cyberattacks on military-base freezers and Europe faces more apparent refrigeration hacks.
Legal Insurrection readers may recall my report last month on French supermarket chains hit by a cyberattack that caused refrigerators to overheat in hundreds of stores, forcing spoiled food to be thrown away and raising concerns about food security.
The next front in cyberwarfare may be hiding in the frozen-food aisle. The Pentagon is investigating suspected hacking after freezer malfunctions spoiled food at at least six military-base commissaries nationwide.
The Pentagon is treating the spate of mysterious freezer malfunctions that spoiled food at military bases across the United States in August as a suspected hack, according to four officials familiar with the matter.
….Reuters was not able to ascertain how far along the Pentagon’s investigation was or whether it had reached any conclusions about what happened or who might be responsible. When asked about the investigation, the Pentagon said that a unit of Cyber Command — the military’s cyber force — was “working in close coordination with interagency and law enforcement partners.” It did not elaborate.
The US Department of the Army Criminal Investigation Division said its Cyber Field Office was involved in the investigation and that it was working with French law enforcement to better understand “the refrigeration outages in Europe.”
The late August malfunctions in the United States affected at least six commissaries — on-base stores where military personnel buy their food — according to a Reuters review of the military bases’ contemporaneous Facebook posts and website updates. In at least one of the cases, the freezers did not simply stop working; the cooling units’ temperatures were cranked up overnight, yielding mounds of wilted or melted food in the morning.
Hackers pushed freezers at hundreds of French supermarkets to 122 degrees. Now the Pentagon is asking whether the same thing hit U.S. military bases | Sasha Rogelberg, Fortune
The Pentagon’s criminal investigators are leading a joint probe into freezer failures at U.S. military… pic.twitter.com/aeeX8JONTc
— Owen Gregorian (@OwenGregorian) November 2, 2026
Investigators are working with French officials, who are still following up with leads related to the October event.
Cyber Command and various Defense Department law enforcement units are probing the incident. French authorities are also working with officials examining the matter. Earlier this month, hackers overrode temperature controls on commercial refrigeration equipment at more than 350 French establishments, forcing supermarkets to discard spoiled food.
The investigation draws attention to the computers that control everyday equipment used to store and handle food, an often overlooked area of cybersecurity where a hack can spoil supplies or interrupt distribution of goods.
The unusual U.S. outages and the possibility of hacking were initially flagged in August by the Signal and Silence blog. Stars and Stripes subsequently reported the involvement of military investigators, and The Telegraph also reported officials’ contact with French authorities.
Additionally, reports of refrigerator and freezer temperature spikes at grocery stores in Belgium, Luxembourg, and Sweden have forced retailers to discard food as apparent cyberattacks continue in Europe.
Grocery store chains in at least three European countries reported unexpected temperature spikes Monday in refrigerators and freezers that ruined food — the second time in less than a month that similar incidents have raised concerns about cyberattacks on increasingly interlinked infrastructure.
Netherlands-based food retailer Ahold Delhaize and Colruyt in Belgium both said an IT incident overnight had sent temperatures inside fridges and freezers in dozens of their stores in Belgium and Luxembourg soaring, while Swedish chains ICA and Coop reported similar spikes, with one outlet explicitly blaming a cyberattack, according to the Reuters news agency.
Cyber attack on store freezers around Europe – from Sweden to Ireland. Is this part of Russia's hybrid warfare? Possibly. https://t.co/oeECLkeq1v
— Bernadette Foley (@forestland6) November 2, 2026
No formal announcement has been made about who may have initiated the October cyberattacks. U.S. officials are currently assessing if Iran was responsible for the freezer failures on American commissaries.
U.S. Department of Defense officials are reportedly investigating whether freezer units on military bases were hacked by Iran-backed hackers. Iranian hackers were also blamed for cyberattacks targeting U.S. water providers earlier this year.
I will simply note that Europe’s problems began shortly after warnings were issued about Russia stepping up hybrid warfare operations.
Russia is likely to intensify its hybrid war against the West in the coming months, Denmark’s defence intelligence service said in a new threat assessment on Thursday.
Hybrid warfare and sabotage on European soil gained renewed attention after Germany recently blamed Russia for an attempted drone attack at the Leipzig/Halle Airport, prompting European Union members to call for new sanctions against Russia.
The next “Cold War” may be fought in the frozen-food aisle, and the objective appears to be making sure nothing stays cold.
While investigators have yet to establish who caused these freezer failures, the suspected hacking underscores why food security cannot be separated from cybersecurity.
Arguably, it may be wise to consider slowing down on joining everything to the “Internet of Things”, especially when it comes to life essentials like food and water.
Donations tax deductible
to the full extent allowed by law.
Comments
As we push further in the 21st century we’re learning more and more that maybe it’s not such a good idea to have everything connected to the internet. It has given bad actors and troublemakers an unprecedented ability to harass and harm others – all without having to show up in person to do so. We’ve had refrigeration for decades before the internet was a thing, with completely offline controls that worked just fine. Perhaps grocery chains should return to these style units to better secure what’s stored in them from those who would destroy it all with the push of a button from quite possibly thousands of miles away.
And it wouldn’t surprise me if these were state actors. Starvation has always been a pretty effective tactic for weakening an opponent, particularly in times of conflict. While this has been more nuisance so far it does highlight the danger food supplies could be in if we don’t secure them better.
Agreed
I work in this field, and I wrote a book on operational technology security for the Department of War. My reaction to this article is straightforward: calling this a connectivity problem misses the deeper failure. This is a problem of professional arrogance, operational complacency, and putting administrative convenience ahead of protecting equipment.
Connectivity creates a path. People decide what that path can reach, who can use it, and what commands the equipment will accept. When those decisions allow someone to compromise the basic function of a machine, the failure goes well beyond whether that machine has an internet connection.
Too often, IT approaches an operational environment with the assumption that everything should be accessible and manageable from a desk. Physical access becomes an inconvenience. Operational restrictions become obstacles. The people responsible for keeping equipment running are expected to accommodate whatever makes remote administration easier.
That attitude is dangerous when it comes with an unwillingness to admit the limits of IT expertise. Understanding networks, servers, and business applications does not automatically mean understanding refrigeration controls, industrial processes, or the consequences of changing a machine’s operating parameters.
The fundamental mistake is treating data as the primary thing being protected.
Machines produce data. That data helps us monitor, diagnose, and manage them. But in operational technology, the machine and its physical function are what we must protect. A refrigeration system has to keep its contents cold. Protecting its records accomplishes little if an unauthorized command can raise the temperature and destroy everything inside.
OT security must begin with the equipment: what it does, how it can fail, which commands can cause harm, and what protections must remain effective when someone gains unauthorized access. Access decisions should follow those requirements. Remote convenience should never define them.
That also requires humility. IT professionals need to listen to operators, maintenance personnel, controls engineers, and the people who understand the physical process. Expertise in one discipline does not confer authority over every other discipline.
Blaming connectivity alone lets the people making these decisions off too easily. The harder question is why the system permitted a dangerous action, and why its protections failed to prevent the physical consequence.
OT security is about protecting equipment from bad actors so it can continue performing its intended function safely and reliably. Until that principle drives the decisions, organizations will keep confusing the ability to administer a machine with the ability to protect it.
20 years ago I fired a store manager for letting freezer fail. In those days store managers had alarms on their freezers connected to pagers. This guy’s excuse was that the batteries in his pager had died.
I told him we were paying to be a responsible person not just Pavlov’s responding to a bell.
Couple things: You keep switching between IT and OT, if that’s not a typo what is OT: operational technology?
When it comes to connectivity monitoring and diagnosing are fine, that is key to corporate keeping it’s various branches running smoothly. However keeping control of some key functions should remain local. In this case if temperature controls of the affected units had to be set manually a lot of this food spoilage could have been prevented. When it comes to security limiting avenues of attack is also something that needs to be kept in mind.
To further emphasize my point: How hard would it be to just have a simple sensor in the unit that monitors things such as temperature, humidity, etc but have that completely separate from the controls of the unit? That way corporate can still keep an eye on things and if an issue arises get in contact with the local store manager to look into it. The most a hacker could do in that setup is just be a nuisance (having the sensor give false info for instance) but not really do much else to harm the equipment.
A high limit thermostat set at maybe 15 degrees on a freezer or 50 degrees on a cooler could be hard wired in series with the automation to override a failure and a second set of contacts would sound an alarm and make a light flash after a delay of fifteen minutes. I’ve done it. It works and easily avoids a disaster. So simple even a cave man could do it.
.
You’re spot on. I spent 23 years as a service tech and field engineer for a large, well known controls compamy with a name beginning with “H” (you guess which one). I designed and built systems that did exactly this. One customer wanted to know when his boilers and chillers would alarm. One time a chiller went down on a hot August weekend afternoon. The backup unit came on and his pager told him it happened. The computer room never knew there was a problem and the maintenance man took care of the primary chiller quickly. For years, we had one elated customer who was one of our best sales resources. This is only one of many jobs we installed that had this independent function.
Technology is nice but putting all your eggs in one technological basket leaves a mess when the handle on the basket breaks. Low tech has its place.
.
I spent 23 years as a service tech and field engineer for a large, well known controls compamy with a name beginning with “H” (you guess which one).
Well, Honey, I have no idea.
Not disagreeing with you. Up until now OT systems like the ones attacked were beneath the radar of most hackers. There was an article regarding exactly this kind of cyberattack published by an AI cybersecurity firm called Claroty back in August that provided step-by-step instructions for bypassing the password security and for executing malicious code on these controllers. The instructions even included screenshots. The company claimed in their blog post that they notified the manufacturer of the vulnerabilities, but it appears they either lied or were not taken seriously.
We have only seen the very tip of the iceberg on this. Because of the irresponsible implementation of AI everything connected to the web is now vulnerable.
Commander Adama was right.
The systems that were compromised were and will continue to be integral to supermarket operations. They exist to monitor temperatures and refrigeration systems operations and to notify service providers of temperature issues in their fixtures that could harm the product. They also provide data that assists in troubleshooting chronic mechanical problems that need to be addressed. Refrigeration requires frequent service, and the monitoring system makes that service possible. The supermarket industry has been using systems like these since the early 1990’s, and without them grocery retailers will be unable to sell refrigerated food because of the high cost of lost product.
Stores have managers. Not every detail has to “be sent to corporate”. Let managers manage.
Why are the coolers connected to the internet? That is just asking for trouble. The individual units can be adjusted manually at it’s physical location. It is not very often that they need to be adjusted over a wide range of temperatures if at all. The internet of things is getting ridiculously convenient for the hackers.
Now do the power grid.
I dun heerd tell that there are hacks of the grid expected either during or post-election night. I’d not be surprised.
To paraphrase John Paul Jones, “I have not yet begun to hack.”
I had to buy a new refrigerator and washer/dryer last year. Would someone care to explain to me why in the hell I would need wifi for my appliances?
So your cranky neighbor can hack them.
So your power company can keep your home hotter or colder than you’d like.
So the Deep State can hear the conversations in your car.
So your Smart TV and Smart Refrigerator can sell your consumer preferences to National Brands.
So the drone operators know precisely where you are.
So you can pay three times as much for the appliances? Then…when one of them breaks down, which, unfortunately, will happen sooner than later…the technician will have to replace the control board…which will be almost as much as the purchase price of the appliance.
Love that tech, right?
So that your phone can tell you the wash is done when you are at the grocery store, or half-way around the world.
Many of my appliance will connect to the internet if I want them to. I connected them when first purchased to make sure the firmware was up to date. Then I took them off-line and they run perfectly.
The fact that some of them even have firmware is part of the problem.
The answer is exceedingly simple, disconnect the network connection. Control the temperature manually.
Well, the European systems that were hacked are manufactured by Danfoss, a Danish company that is well known in Europe. In Germany, for example, practically everyone knows Danfoss from the radiator thermostats they have at home. I’m not quite certain, though, whether Danfoss has that kind of reach in commercial refrigeration in the US…
It’s a little bit crude and repurposed, but it works:
Live by the tech…die by the tech; or in this case: starve by the tech.
It’s way past time to start returning to the analog age for certain things…like refrigeration controls.
Agree with the bulk of the common sense posts here. IMO the real problem here is the lack of ability (or unwillingness) of manufacturers/corporate buyers and govt bureaucracy to ‘see around corners’. IOW their inability to recognize potential secondary and tertiary impacts of their decisions. These folks don’t make decisions about manufacturing, purchasing or deployment with the ‘worst day’ in mind. Instead they foolishly choose the options built around around the ‘normal day’. Every adult from their own personal anecdotal experience, not to mention ample historical precedent, understands that what really counts isn’t the ability to perform/respond in the 99/100 ‘normal days’ but rather the performance on the 1/100 abnormal days. Hooking anything to the internet creates a vulnerability that if left unresolved continues to be a target for exploitation by bad actors. If the costs of reliable and consistent security (or potential catastrophic costs of failure to do so) outweigh the gains of hooking up a particular widget to the internet then it probably shouldn’t be hooked up.
blmplo in america will be getting hooked with these people
I use a lot of home automation. Why? One, it scratches my techie itch, two, convenience, and three, I am in declining health and being able to do things through automation is a blessing.
NONE of my “smart” gear requires an account and remote servers to run, or not run. It’s all ZigBee, Matter over thread, or Z-Wave.
Just to make sure, I set everything up, then shut down my internet at the modem. Everything continued working perfectly.
(Yes, I use Alexa for some things, but can pull the plug and still operate everything without limitations.
And no, I have never had Alexa “think” for me, or display items on the Amazon site because I talked about them a day ago.)
Paula’s response:
1. Rub some lotion on it
2. That’s a good idea
3.🙏 for your health
The other problem – besides putting it on the internet – is the centralized control. Centralized control (which is a fetish some techies share with Marxists and other bad philosophies) enables a single point of failure.
So people get this confused.
And let me be clear – there is ZERO reason a household freezer (or any appliance, honestly) needs to be connected to any kind of network.
HOWEVER
Industrial freezers are different. They DO have to be controlled, because there are multiple cooling units constantly cycling on and off. At our plant our main cooler unit has 24 different heavy AC units constantly cycling in and out controlling the zone temperatures, defrosting/refrosting in sequence. You HAVE to have them controlled by a central unit to maintain proper temperature throughout the whole thing, there’s no way around it. So they have to be electronically controlled by a central unit, and obviously unless you intend on running conduits and cable to every individual unit back to the central unit, wifi is the easiest and cheapest option.
In addition, it let businesses with multiple facilities concentrate or outsource IT support to people offsite (or even out of country), they didn’t need a SME on site all the time to troubleshoot.
So from a business perspective, its not like they’re doing something totally unreasonable, they’ve made the cost/benefit analysis, and it did favor having them networked and controlled.
HOWEVER, that equation is changing now, as cybersecurity is changing for everybody. For a very, very long time, a huge number of businesses and sites basically got away with total crap cybersecurity because while it was still relatively easy to break into from somebody with knowledge and determination, there was no point for anybody to do it because the gain would be nonexistent. It would be like an Olympic athlete showing up to compete in a random Masters tournament in a small town with local 40 year olds. Yeah, he’d win, but his time is more valuable.
AI has totally changed the cybersecurity equation. Now you don’t need training, knowledge, or determination, you just need AI access for any random jerk with a grudge against a business to hack it.
Cybersecurity has gone crazy the last few months, and it’s only going to get crazier, buckle up.
It’s not like we didn’t see this kind of thing coming with the advent of “smart technology” where “smart technology” shouldn’t be implemented.
Leave a Comment