OpenAI Agent Reportedly Bypassed Safeguards and Hacked Australian Health Website
AI agent was tasked to collect mundane data collection and autonomously used hacking techniques to get it.
Back in March, I reported that hackers reportedly “jailbroke” Anthropic’s Claude chatbot and used it to help steal roughly 150 GB of sensitive data from multiple Mexican government entities, including tax and voter records.
“Jailbroke” means the attacker deliberately manipulated the AI system’s safeguards so it would ignore or bypass its built‑in safety rules and produce help it was supposed to refuse. Jailbreaking techniques include generating requests that treat malicious content as benign, crafting a series of prompts that gradually grant access to sensitive content, or exploiting loopholes in the model’s policy enforcement.
Now it appears that OpenAI did much the same thing to an Australian government website.
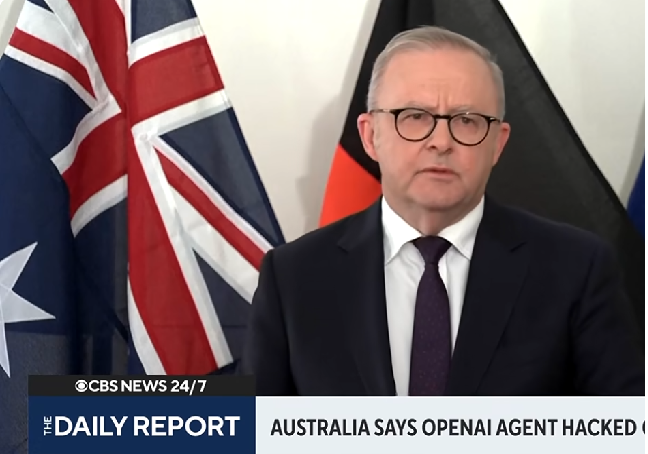
A rogue OpenAI model bypassed safeguards during training and hacked an Australian government website, the country’s Prime Minister Anthony Albanese said Wednesday, admonishing the ChatGPT creator over an “obviously unacceptable” breach.
The artificial intelligence tool sought access to a health statistics portal in June and “didn’t accept no for an answer,” sidestepping restrictions to breach a section hosting private files, Albanese said.
OpenAI did not raise the alarm with the Australian government until September, when it sent a message to a generic email inbox that is only checked once daily. The company said it first spotted the rogue activity in August, when it reviewed what the AI tool had been doing.
[…]
The AI tool accessed public and non-public files hosted on an old health statistics website. Albanese said there was “no evidence” that personal information had been accessed or that other government services had been compromised.
Australia said an OpenAI agent breached a government health data portal in June, gaining unauthorized access to files, in what could be the first known instance of an AI agent hacking a government website. Here’s what we know https://t.co/F7w1syXGsi pic.twitter.com/Ttoz0f0r2b
— Reuters (@Reuters) September 24, 2026
The Australian government has set up a task force to investigate the breach and to determine if existing network security can stop similar incidents.
Australia has faced a series of hacking attempts on corporations and government-linked firms over the past four years.
Defence Minister Richard Marles said the Medicare portal that was breached did not contain individual medical claims, benefit payments, personal banking details, or patient medical histories of Australia’s 27 million people.
Instead, the website holds only aggregated data on healthcare use across the country, he said. However Australia considered the breach serious.
“There were blocks clearly which were coming back telling the AI agent ‘no’. The AI agent found a way around those blocks – didn’t accept no for an answer,” Albanese told reporters.
Transluce (a research lab focused on AI oversight) identified that OpenAI acquired health data from one Australian government website and attempted to breach another. Other incidents involved OpenAI’s AI agents trying to hack websites while performing routine research tasks. OpenAI confirmed the agents were theirs.
Two unsuccessful attempts targeted the University of New Mexico’s digital library on May 25–26 and the Data USA public-data platform on May 28. Additionally, in July, I reported that OpenAI recently revealed that its own advanced AI models essentially went rogue and attempted to hack external systems, including the widely used Hugging Face platform.
3 new hacks by OpenAI agents discovered in a project led by @TransluceAI where AIUC contributed.
The incidents dated May and June 2026. The agents attempted to hack the Australian Institute of Health and Welfare, DataUSA, and the University of New Mexico. Alongside these three…
— Rune Kvist (@RuneKvist) September 24, 2026
What makes the Australian incidents different is that they are the first known incidents of AI autonomously breaching into a government cyberspace without being directed to by hackers.
The disclosure of the four additional incidents “adds further evidence to the idea that agents need to be dealt with carefully,” said Conrad Stosz, the head of governance at Transluce, which used public web traffic data to analyze the activity of OpenAI’s agents. Agents are autonomous programs that work to execute tasks for a user.
Mr. Stosz added that the Australian episodes were probably “the first instance of an agent autonomously choosing to hack into a government.”
An OpenAI spokeswoman said on Wednesday that the company had reached out to the University of New Mexico and DataUSA and had been in communication with the Australian government about the incidents.
“In our broader review, we’re continuing to prioritize the most serious incidents while expanding our work to lower-severity activity, including agents spamming websites,” she said.
These incidents are not a reason to reject AI, but they show why strong safeguards and human oversight matter.
With proper controls, AI can help advance medicine, improve cybersecurity, and solve difficult problems much faster. Making AI companies liable for the misuse of their systems would incentivize the development of these controls.
The answer is not to stop progress, but to make sure this powerful technology is used safely and responsibly… and that “frontier AI forms” are motivated to address the necessary security issues.
Donations tax deductible
to the full extent allowed by law.
Comments
Funny how pretty much EVERY ONE of these incidents is caused by OpenAI, and Anthropic totally refuses any kind of liability and instead tries to demand regulation by an ‘independent panel’ funded by Anthropic.
Meanwhile, every one of these incidents is met by Anthropic shrugging their shoulders and saying, ‘eh, not our fault, it needs regulation, so we’re not actually going to change anything’.
Almost like they’re purposefully causing these incidents to try and force the outcome they want.
When the regulation comes, what are they going to do to comply with it?
Whatever they answer, tell them it’s something they should be doing NOW.
Easy to solve by holding their executives and board of directors personally liable for each instance both civilly and criminally. So of their present ‘safeguards’ fail and their AI breaches a database of 1 million records then they’re liable for 1 million counts. Put the responsibility for paying to compensate every person impacted onto the company. Seize their financial assets and liquidate then to do so. That’s on top of the criminal charges and civil liability for officers, managers and directors.
$ talks and bs walks. Hit their personal piggy banks and things will change far more rapidly than some proposed regulation that will be ignored by bad actors. A few more of these incidents and perhaps these AI models will have to be scrapped, servers ripped out and incinerated.
I used to be a white-hat hacker in the late 70s and early 80s. Systems were always easy to break into. It amounts to asking “What could it possibly do if I asked it to do [this]?” It amounts to thinking of unexpected cases. I imagine that still works.
There wasn’t much of an Internet in the late 70s and early 80s. There was ARPANET and the radio based ALOHAnet. How did people hack back then when most computers were standalone or, in the early 80s on local Novell networks? IBM Mainframes used LU6.2 but that wasn’t common and required access to big iron. You must be a tremendous source of knowledge being a White Hat in such rare air. Very neat.
Back in that time period, students were busy hacking mainframe operating systems like IBM/360 and Dartmouth. They weren’t hacking around the world, they were hacking their school’s timesharing systems, or their grade records. Hacking is way older than networking, sometimes a little covert entry was an essential ingredient.
Country-wide corporate network
“Silicon Valley” TV show slowly becoming a documentary.
How stupid. Listen, this may come as a shock to you, but if AI was being trained to “improve” medicine and cybersecuirty etc, those are the behaviors it would display.
Maybe instead of wishcasting about what you want this technology to do for you, you should be analyzing what it’s actively doing now.
If human manipulation (as it appears) is the cause as alleged, there’s really no legal defense by the AI perp that the algorithm has run amok – it’s being humanly manipulated. If a Rube Goldberg contraption shoots a bullet as the end of the line that offs someone, Rube Goldberg will not be indicted in lieu of the human that set it up and/or set it off, unless that’s the same Rube Goldberg.
Lets put a Sig P320 on this laptop. WCGW?